
Enterprise risk management (ERM) has been a popular term in the risk field for years. Managers often use it to suggest something broader than the traditional risk management function. Yet many professionals can’t clearly explain how the two actually differ.
This article explains what ERM is, how it differs from traditional risk management, the ERM framework and risk response strategies, and the practical challenges of implementing ERM in an organization.
What Is Enterprise Risk Management?
The Casualty Actuarial Society (CAS) defines ERM as:
“The discipline by which an organization in any industry assesses, controls, exploits, finances, and monitors risks from all sources for the purpose of increasing the organization’s short- and long-term value to its stakeholders.”
In simpler terms, ERM covers all the tools and processes an organization uses to manage risks across the whole enterprise, and to seize opportunities. It starts by identifying events that matter to the organization, both threats and opportunities, evaluating their likelihood and impact, and designing responses that add value for stakeholders.
Two widely used ERM frameworks are:
- COSO ERM, from the Committee of Sponsoring Organizations of the Treadway Commission. It was first published in 2004 and updated in 2017 as Enterprise Risk Management: Integrating with Strategy and Performance.
- ISO 31000, the international risk management standard, first published in 2009 and revised in 2018.
A key idea in ERM is that risk isn’t only something to avoid. Taking the right risks is how organizations grow. ERM aims to make sure the risks an organization takes are deliberate, understood and aligned with its strategy.
ERM vs. Traditional Risk Management: Five Key Differences
-
Insurable vs. Non-Insurable Risks
Traditional risk management focuses mainly on risks that can be transferred, usually through insurance, or through derivatives and structured finance where insurance isn’t available.
ERM is broader. It also covers risks that can’t be insured. For example, if a workplace accident injures employees, insurance may cover the financial loss. But the accident also damages the organization’s reputation, which is hard to quantify and can’t be insured. ERM considers risks such as:
- Damage to reputation, including on social media
- Supplier and supply chain disruptions
- Poorly judged mergers and acquisitions
- Strategic risks such as new competitors or changing customer preferences
-
Single Dimension vs. Multiple Dimensions
Traditional risk management tends to focus on a single measure: expected loss (the probability of a risk multiplied by its financial impact).
ERM takes a more holistic view and asks how a risk affects the organization’s strategic goals. Typical ERM questions include:
- Will the risk stay in one part of the organization or spread across functions?
- How quickly will it affect the organization? (This is sometimes called risk velocity.)
- Will its effects be short-lived or long-lasting?
- How prepared are we to respond?
-
Department Level vs. Enterprise Level
In traditional risk management, risk is managed in silos. Each department identifies and manages its own risks. That may make sense for each department, but at the company level, the results can be inconsistent, contradictory and inefficient. Managers sometimes reduce risk in their own area while unintentionally creating risk elsewhere. Risks that span departments may have no clear owner, and resources are wasted on duplicated effort.
ERM takes an enterprise-wide view. Risks are identified, assessed and prioritized consistently across the organization, and decisions serve the organization as a whole rather than any single department. Business units still own and manage their risks day to day, but a central risk function coordinates the approach and gives leadership an integrated picture.
-
Reactive vs. Proactive
Traditional risk management is often reactive: it responds to events that have happened or tries to prevent a repeat of past events, relying heavily on historical data. But many modern risks, such as those from new technologies and fast-changing markets, can’t be understood by looking in the rearview mirror.
ERM is proactive. It uses scenario analysis, emerging-risk reviews and horizon scanning to anticipate how the future might unfold.
-
Standardized vs. Customized
Traditional risk management relies on well-established, standardized processes that cover common risks and often focus on compliance. ERM needs a more customized approach for non-standard risks, combining creativity and judgment with statistical skills.
| Dimension | Traditional Risk Management | Enterprise Risk Management |
|---|---|---|
| Scope | Mainly insurable and hedgeable risks | All risks, including strategic and reputational |
| Focus | Expected financial loss | Impact on strategic objectives and value |
| Organization | Departmental silos | Integrated, enterprise-wide |
| Timing | Reactive, based on past data | Proactive, forward-looking |
| Approach | Standardized and compliance-driven | Customized and strategy-driven |
| View of risk | Something to minimize | Something to manage, including opportunities |
| Ownership | Risk manager or insurance buyer | Board, senior management and all business units |
The ERM Framework
The CAS framework looks at ERM in two dimensions: the types of risk and the steps of the risk management process.
Four Types of Risk
- Hazard risk: natural disasters, fire and property damage, liability claims, and injury or illness to employees.
- Financial risk: foreign exchange, commodity price, interest rate, credit, asset value and liquidity risks.
- Operational risk: failures in processes, people and systems, such as product failures, labor relations issues and poor customer service.
- Strategic risk: competition, changing demand and prices, regulatory and political trends, social trends and access to capital.
Seven Process Steps
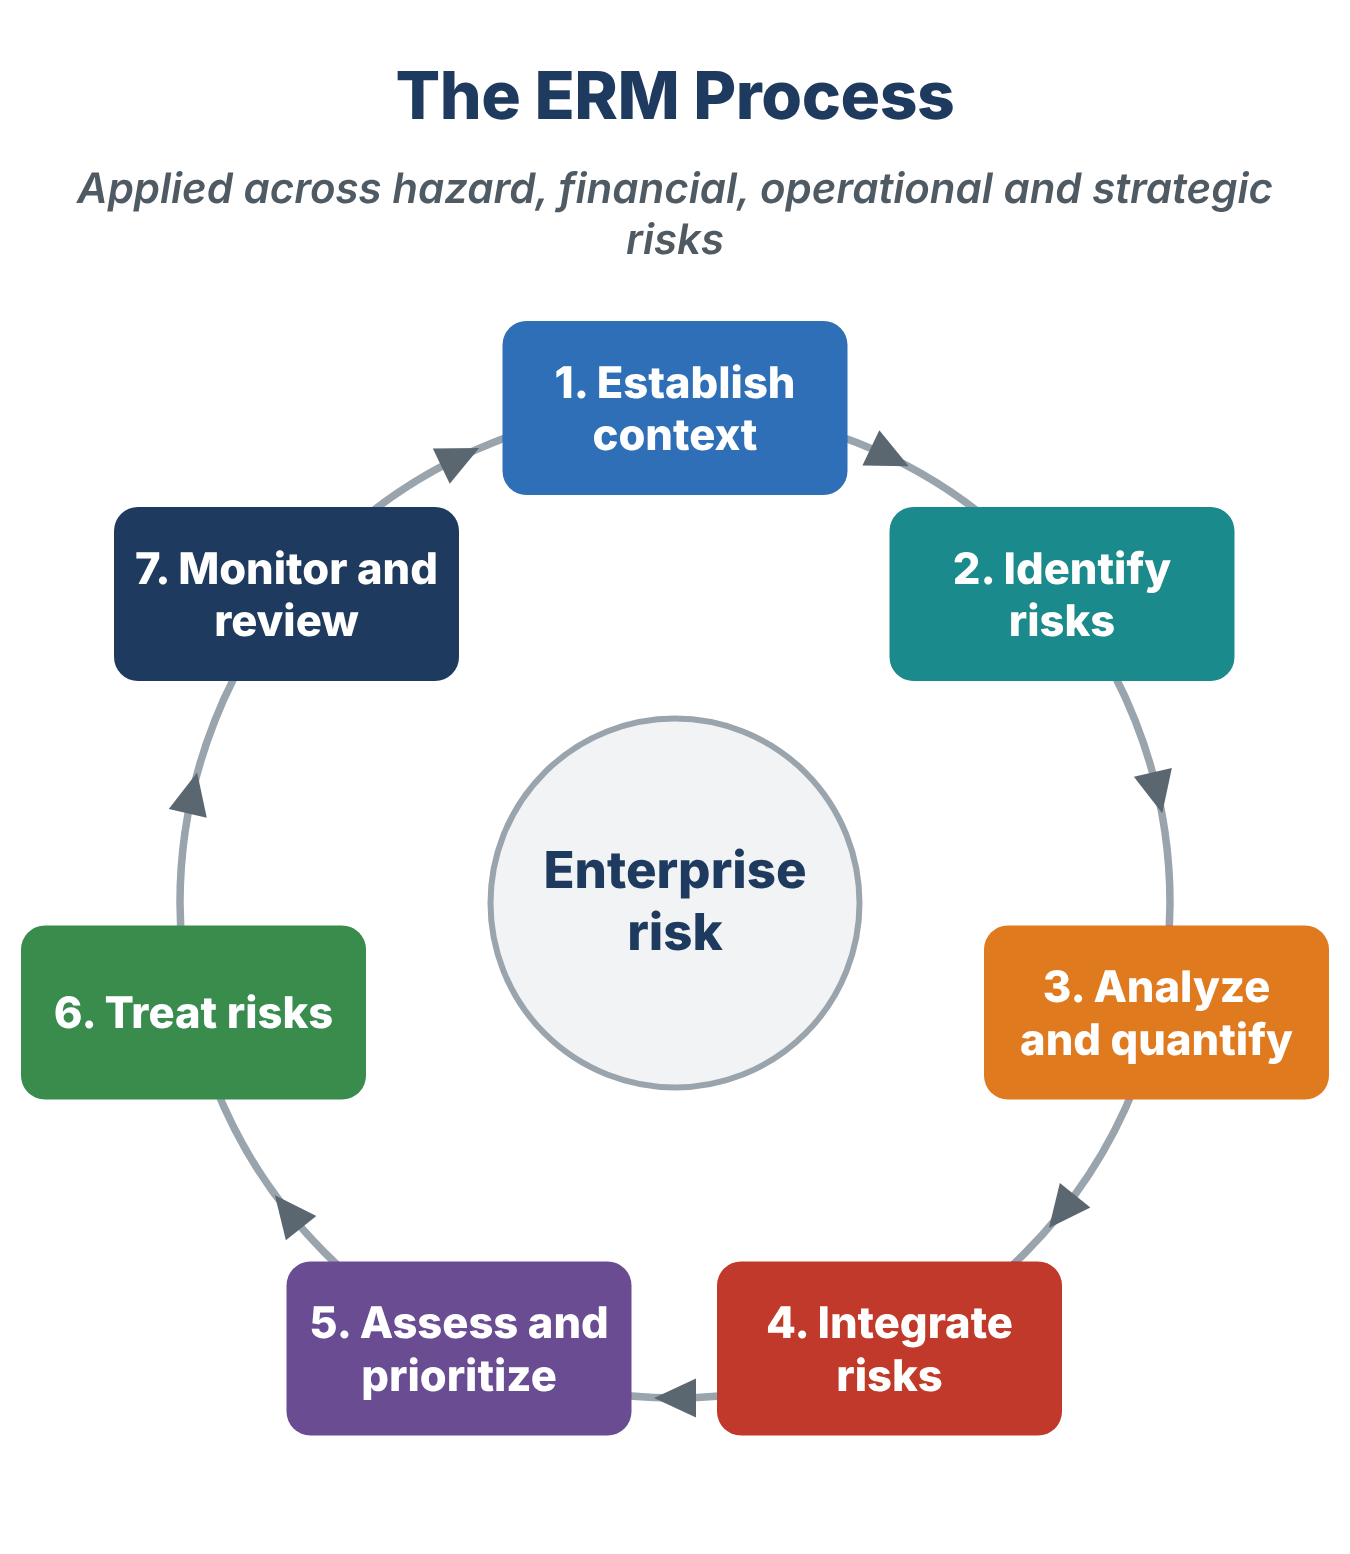
- Establish context: understand the environment in which the organization operates and its objectives.
- Identify risks: find the threats and opportunities that could affect those objectives.
- Analyze and quantify risks: estimate the likelihood and impact of each.
- Integrate risks: combine risks to understand their combined effect and how they interact.
- Assess and prioritize risks: rank risks against the organization’s risk appetite.
- Treat risks: choose and implement responses.
- Monitor and review: track risks and responses, and adjust as conditions change.
Each of the seven steps applies to each of the four risk types, forming a grid that helps make sure nothing is overlooked.
| Process Step | Hazard | Financial | Operational | Strategic |
|---|---|---|---|---|
| Identify | Site inspections, loss history | Exposure reports | Process mapping, incident logs | Competitor and market analysis |
| Analyze and quantify | Catastrophe and loss models | VaR, sensitivity analysis | Loss data, key risk indicators | Scenario analysis |
| Treat | Insurance, safety programs | Hedging, limits | Controls, training, backup systems | Strategic plans, diversification |
| Monitor | Claims and incident trends | Daily risk reports | Audit findings, KRIs | Board strategy reviews |
Risk Response Strategies
Organizations typically choose among four responses:
- Avoid (exit): stop the activity that creates the risk.
- Reduce: take actions that lower the likelihood or impact of the risk.
- Share or transfer: pass part of the risk to others, for example through insurance, hedging, outsourcing or joint ventures.
- Accept: take no further action, usually because the cost of mitigation outweighs the benefit, and the risk is within the organization’s appetite.
Practical Considerations in Implementing ERM
Deciding to adopt ERM is the easy part. Implementing it successfully is harder. These considerations apply in most organizations.
-
Appoint an ERM Champion
Someone must lead the initiative, often a chief risk officer (CRO) who reports to the CEO or CFO and has regular access to the board or its risk committee. The CRO needs a capable team that acts as a change agent and is accountable to senior management.
-
Build ERM into the Culture
Traditionally, each department handled its own risks. Finance handled financial risks, IT handled technology risks and marketing handled strategic risks, each with its own reporting line, tools and measurement scales. ERM requires these groups to work together using a common language and consistent methods. Some managers may feel threatened and become defensive, so leaders need to explain the benefits, train people and reward cooperation.
-
Identify the Unthinkable
Visible risks are relatively easy to plan for. The greatest damage often comes from risks nobody anticipated. The 1982 Tylenol tampering case, in which cyanide-laced capsules killed seven people, is a classic example of a risk few in the pharmaceutical industry had considered. Good risk assessment deliberately challenges assumptions and imagines unlikely events.
-
Quantify Strategic and Operational Risks
Hazard and financial risks are relatively easy to quantify. Strategic and operational risks, such as poor use of knowledge or an unnoticed inefficiency that slowly erodes output, are much harder. Qualitative methods, such as expert judgment and risk scoring on likelihood and impact scales, help rank these risks.
-
Integrate Different Risks
It’s difficult to know exactly how different risks interact. Past relationships may not hold in the future, especially in a crisis, when risks that seemed unrelated often move together. Organizations should build models that can be improved over time and test them with stress scenarios.
-
Recognize the Limits of Risk Transfer
Insurance and capital markets offer many ways to transfer hazard and financial risks, but they have limits. For many operational and strategic risks, such as reputational damage or loss of market share, few transfer options exist, so these risks must be managed internally.
-
Monitor Continuously
ERM isn’t a one-time project. Risks and responses must be monitored continuously, reports should compare current assessments with previous ones, and strategies must be updated as the risk environment changes.
How to Get Started with ERM: A Step-by-Step Guide
- Secure board and CEO support. ERM fails without visible leadership commitment.
- Define risk appetite. Agree on how much risk the organization is willing to take in pursuit of its goals.
- Choose a framework. Adopt COSO ERM or ISO 31000 and adapt it to your organization.
- Build a risk register. Record key risks, owners, ratings and responses in one place.
- Use a common scale. Rate every risk on the same likelihood and impact scales.
- Link risk to strategy. Review risks alongside strategic plans and major decisions.
- Report regularly. Give the board a concise, integrated view of top risks and trends.
- Review and improve. Learn from incidents and near misses, and update the program.
How to Build and Maintain an Enterprise Risk Register
A good risk register turns ERM from policy into day-to-day decision-making. Build and maintain yours in four steps:
-
Use One Scoring Scale
Use the same 1-to-5 scales across the organization for likelihood (from rare to almost certain) and impact (from negligible to severe).
Define financial, operational and reputational thresholds for each level, so all departments score risks the same way.
-
Record the Same Details for Every Risk
Each entry should include a unique ID, a clear description, the inherent risk score, the existing controls, the residual risk score and one named owner. Assign a person, not a team.
-
Add Key Risk Indicators
Link each major risk to a measurable early-warning sign. For example, link “IT infrastructure failure” to “server capacity above 85% for three days in a row.”
-
Review Monthly and Escalate
Ask risk owners to update progress each month.
Escalate any risk whose residual score is rising to senior management and the board.
Conclusion
Enterprise risk management is a broader, more integrated and more strategic approach than traditional risk management. It covers insurable and non-insurable risks, looks beyond expected loss to strategic impact, breaks down departmental silos, anticipates future risks and adapts to each organization’s needs. The ERM framework combines four risk types, hazard, financial, operational and strategic, with seven process steps. Implementing ERM requires strong leadership, cultural change, better ways to assess hard-to-measure risks and continuous monitoring. More and more organizations are adopting ERM because it helps them protect value and create it.
Frequently Asked Questions
What is enterprise risk management?
ERM is an integrated, organization-wide approach to identifying, assessing, managing and monitoring all types of risk, and to taking advantage of opportunities, in order to increase value for stakeholders.
How is ERM different from traditional risk management?
Traditional risk management focuses on insurable risks managed within departments, often reactively. ERM covers all risks across the enterprise, is forward-looking and links risk to strategy.
What are the four types of risk in the ERM framework?
Hazard, financial, operational and strategic risk.
What are the four risk response strategies?
Avoid, reduce, share or transfer, and accept.
What does a chief risk officer do?
A CRO leads the ERM program, coordinates risk management across the organization and reports on key risks to senior management and the board.